Security Information & Event Management

Real-time threat visibility
across your enterprise.

Our SIEM service covers the full lifecycle - from platform selection and deployment through to ongoing optimisation, tuning, and managed detection support.

Real-time monitoring and alerting for threats
Centralised log management from diverse sources
Advanced analytics for detecting complex incidents
Automated response and threat intelligence integration
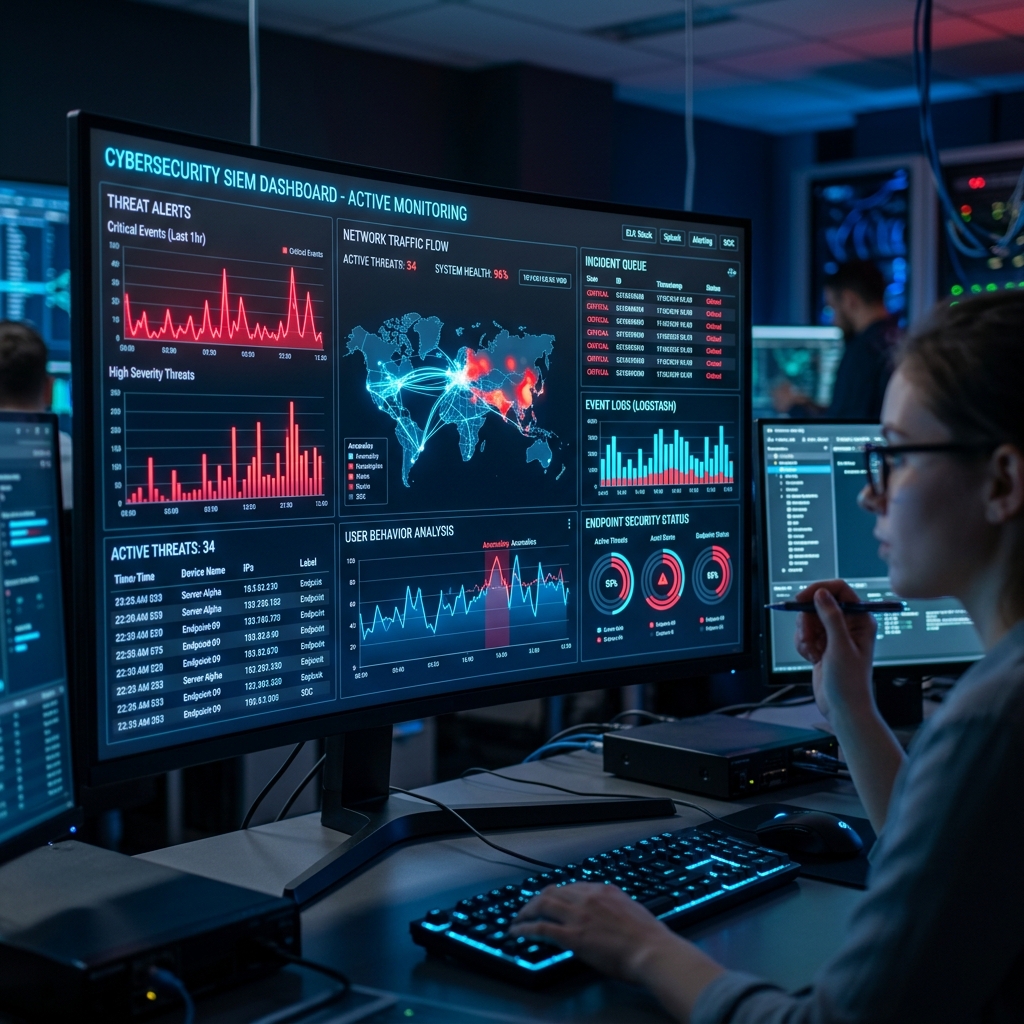
Cybersecurity Operations

100% Threat Visibility

Uncover hidden attacks with precision-tuned real-time detection.

Service Overview

What our SIEM service delivers.

A Security Information and Event Management platform is only as effective as its configuration. Most organisations over-invest in technology and under-invest in tuning, or deploy a SIEM and leave it largely unused. Rutters changes that. We design, deploy, and continuously optimise SIEM environments to surface genuine threats - not alert noise.

Rutters Solutions Ltd partners with leading SIEM solution providers to offer best-in-class products, ensuring robust and scalable security operations. Our portfolio includes trusted platforms that let you monitor, detect, and respond to threats efficiently - giving you complete visibility across your network, streamlined operations, and stronger compliance and risk management across your infrastructure.

Every engagement is led by a named senior consultant with direct, hands-on experience in this domain. You will always know who is accountable for your work - and have direct access to them throughout.

Discuss Your Requirements

Key Deliverables

  • Detailed gap analysis of current log coverage and detection capability
  • Custom detection rule library tuned to your environment and threat model
  • Executive and operational dashboards tailored to your stakeholders
  • Incident response playbooks and escalation procedures
  • Full documentation, configuration records, and knowledge transfer

Technology Partners

Supported SIEM Platforms

We work across the leading SIEM platforms - selecting or optimising the right fit for your environment, not pushing a single product.

IBM QRadar
IBM QRadar
Microsoft Sentinel
Microsoft Sentinel
Logsign
Logsign
Elastic
Elastic
SGBox
SGBox
LogRhythm
LogRhythm

Why It Matters

Key Benefits

The core reasons a well-tuned SIEM programme is foundational to modern security operations.

Enhanced Threat Detection

Precision-tuned detection rules that surface real threats and suppress noise, giving your SOC team the focus they need.

Centralized Security Visibility

Unified log aggregation and correlation across your entire estate - cloud, on-premises, hybrid, and third-party systems.

Faster Incident Response

Pre-built playbooks and escalation paths that compress the time from detection to response - critical when seconds matter.

Compliance & Reporting

Custom dashboards mapped to ISO 27001, DORA, NIS2, and PCI DSS control sets for confident regulatory reporting.

How SIEM Works

The operational workflow behind every alert.

From raw log data to a resolved incident - how your SIEM platform continuously protects your environment.

01

Log Collection & Ingestion

Data is aggregated from endpoints, network devices, cloud services, and applications into a centralised platform.

02

Normalisation & Correlation

Disparate log formats are normalised and correlated to reveal relationships between events across sources.

03

Threat Detection

Rule-based logic and advanced analytics identify anomalies and known attack patterns in real time.

04

Alert Triage & Prioritisation

Detections are scored and prioritised so analysts focus on what matters - not chasing false positives.

05

Investigation

Analysts examine context, timelines, and related events to confirm or dismiss each prioritised alert.

06

Response & Remediation

Confirmed threats are contained and remediated, with automated response and threat intelligence integrated throughout.

How We Work

Our Methodology

A structured, proven approach built on years of practitioner experience - transparent at every stage.

Phase 01

Discovery & Assessment

Audit your existing log sources, detection coverage, and current SIEM configuration to identify gaps and tuning opportunities.

Phase 02

Architecture & Design

Define data architecture, log ingestion strategy, retention policy, and detection rule framework aligned to your threat model.

Phase 03

Deployment & Tuning

Configure and tune detection rules - iteratively reducing false positives while increasing signal fidelity across all log sources.

Phase 04

Reporting & Handover

Deliver executive dashboards, operational runbooks, and a full handover package with knowledge transfer for your internal team.

Why Rutters

Senior expertise. No shortcuts.

Every SIEM engagement we deliver is led by a practitioner with direct, hands-on experience in this domain. We apply rigorous methodology and communicate findings in a way that drives real action - from technical teams to board level.

Rutters has the experience, skillset, and commitment to successfully launch and lay the foundation for a successful SIEM programme. Our certified consultants carry out assessments, deployments, fine-tuning, customisation, and maintenance across LogRhythm, Splunk, and IBM QRadar SIEM architectures - backed by a proven track record of completed cybersecurity projects and deep technical expertise across networking devices, operating systems, and security subsystems.

Request a Proposal

Senior-Led

Delivered by practitioners with years of specialist experience, not delegated to junior staff.

Vendor Neutral

No product affiliations. Our recommendations are based entirely on your risk profile and objectives.

Clear Reporting

Deliverables calibrated to technical teams and executives alike - actionable, not just comprehensive.

Post-Delivery Support

We remain available after delivery to support remediation and answer questions as your team acts.

Ongoing Support

Rutters' Expert Support Benefits

Deployment is only the beginning. Our support continues long after go-live.

24×5 Expert Technical Support

Direct access to experienced SIEM practitioners throughout the working week - not a ticketing queue.

Personalised Onboarding & Configuration

Every environment is different. Onboarding and configuration are tailored to your infrastructure and risk profile, not templated.

Tailored Use Case Development

Detection use cases built around your specific threat model and environment - not a generic, one-size-fits-all rule set.

Ready to Start?

Let's discuss your security requirements.

Every engagement begins with a confidential, no-obligation conversation. We will respond within one business day and confirm the right next step.

All enquiries are treated in strict confidence.